
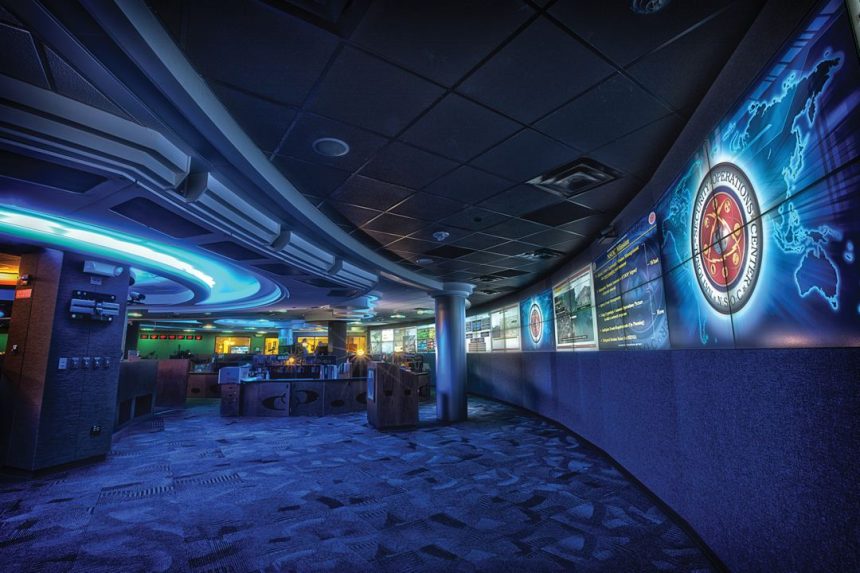
A security operations centre can receive tens of thousands of alerts in a day, and the overwhelming majority are harmless: a mistyped password, a software update behaving oddly, an employee logging in from a new café. Buried in that noise may be the first sign of a genuine intrusion, and tired analysts asked to judge everything will eventually miss something. Centres are therefore teaching software to perform first triage the way a good analyst would, gathering context before deciding what deserves human attention. Modern triage systems correlate an alert with asset records, recent changes, threat intelligence and the user’s normal patterns, then either close the obvious false alarms, enrich and queue the ambiguous cases or escalate the genuinely suspicious within seconds. The aim is not to remove analysts but to protect their attention for investigation and response, the work machines do badly. Early adopters report large reductions in queue volume, though they warn that badly tuned automation can just as efficiently discard a real attack. That risk drives a discipline of sampling: analysts audit a slice of automatically closed alerts every day, and every automated decision must be explainable enough for a human to reconstruct later in an incident review or a courtroom.
What the Evidence Shows
The change is reshaping the analyst’s job rather than abolishing it. Junior staff once spent their first years clearing repetitive alerts; now they are trained sooner in hunting, forensics and communication with the wider business during incidents. Vendors compete on how transparently their systems reason, because security leaders have learned to distrust confident black boxes in a field where adversaries actively probe for blind spots. Attackers adapt too, shaping their activity to look like the benign noise that triage systems are trained to dismiss, which is why the audit loop and periodic red-team testing matter as much as the software itself. Centres also share anonymised triage outcomes through industry groups, so a pattern recognised at one organisation can sharpen filters elsewhere without exposing sensitive details. Regulation is catching up, with incident reporting rules that assume fast, well documented detection. Measured honestly, automated triage is neither magic nor menace: it is a way of spending scarce expert attention where it counts. The centres that benefit most treat it as a junior colleague under supervision, fast, tireless and fallible, whose work is checked and whose mistakes feed back into training for the whole team. Reporting and analysis from sources such as IEEE Spectrum track the same developments, and specialists following automated triage in security operations centres say the direction is now consistent across independent lines of evidence.
The Wider Context
Adoption of automated triage in security operations centres follows a familiar pattern with an unfamiliar speed. Early users tolerate rough edges in exchange for advantage, mainstream users arrive when the tool disappears into existing workflows, and the market consolidates around whoever made that transition feel effortless. Vendors are racing less on raw performance now than on integration, support and trust.
What Happens Next
The realistic forecast for automated triage in security operations centres is steady integration rather than sudden replacement: embedded in products people already use, improving in increments, and regulated in proportion to its reach. The companies and institutions that plan on that basis, training staff and redesigning processes instead of chasing launches, are the ones the adoption data tends to vindicate. You can follow related developments in our coverage of technology.
It is also worth remembering how quickly the picture in this area has changed before. Positions that looked settled a few years ago have been revised as new data arrived, and the same humility is appropriate now. The strongest coverage of this subject, and the most useful advice, tends to come from sources that update their views openly when the facts move, rather than defending an earlier position long after it has stopped fitting the evidence available.